
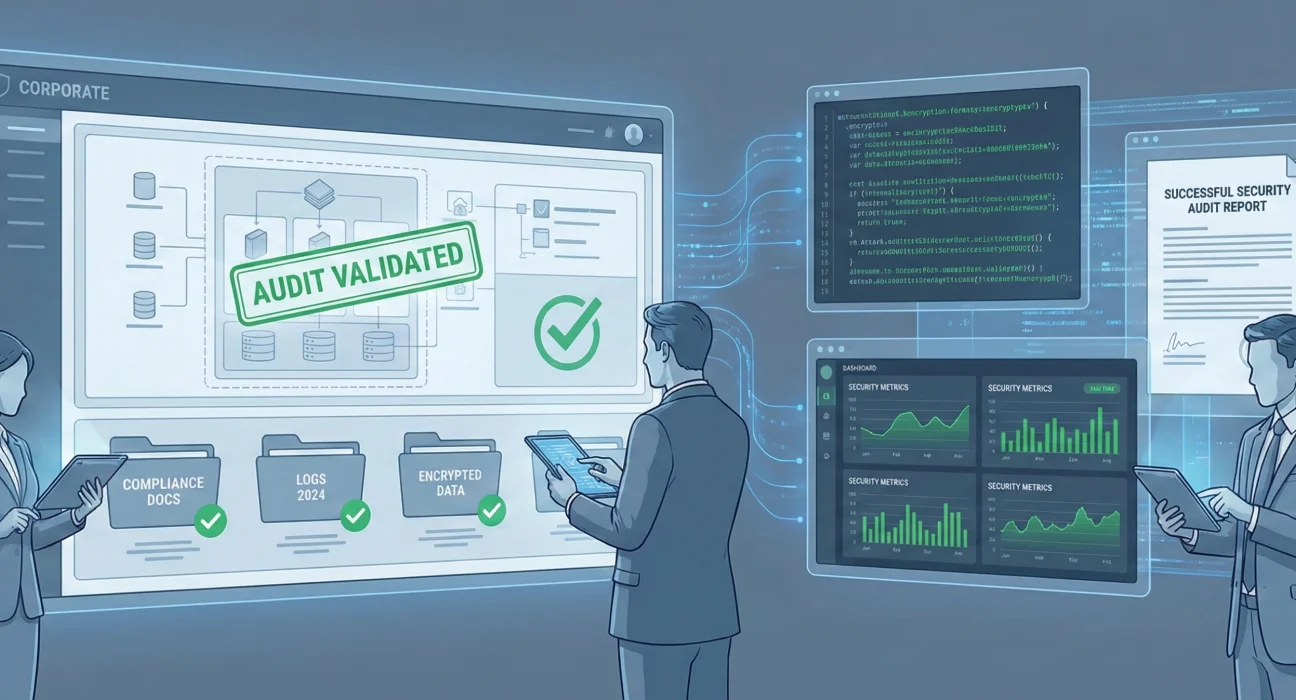
Security audits are a fact of life for enterprise applications. Regulators require them. Board members ask for them. Partners and customers demand them. Insurance providers condition coverage on them.
Yet many large enterprises approach security audits with a sense of dread. Audits become stressful events that reveal gaps, trigger emergency fixes, delay launches, and consume enormous management attention.
The audit itself is rarely the problem. The problem is that the application was not built with audit readiness in mind.
When security is treated as something to verify at the end rather than something to build throughout, audits become crisis management exercises. Findings pile up. Remediation timelines stretch. Go-live dates slip. Stakeholder confidence erodes. What should have been a validation checkpoint becomes a program risk.
For C-level executives overseeing enterprise software delivery or large-scale digital transformation, the question is not whether your applications will be audited. They will. The question is whether you are building applications that pass audits on the first attempt or building applications that require expensive remediation cycles.
Why Security Audits Fail And What That Costs
Security audits fail for predictable reasons. Most have nothing to do with auditors being unreasonable or standards being unclear. They fail because of execution gaps.
Security is designed in isolation. In many programs, security is a separate workstream managed by a separate team. Developers focus on features. Security teams focus on controls. The two groups meet at formal review gates. By then, fundamental design decisions are locked. When auditors find gaps, inadequate access controls, missing encryption, and poor logging, fixing them means rearchitecting components that were considered complete.
Evidence is gathered retroactively. Audits require documentation, architecture diagrams, security policies, risk assessments, test results, and change logs. Many enterprises scramble to produce this evidence when the audit is scheduled. Documents are created to satisfy the audit rather than created naturally as part of delivery. Auditors recognise this. Retroactive documentation lacks detail, contains inconsistencies, and often does not match actual implementation.
Testing is incomplete. Functional testing validates that the application works. But security testing, penetration tests, vulnerability scans, and code analysis often get deferred. When auditors ask for evidence of security testing, teams have little to show. Or worse, they conduct rushed testing right before the audit, discover issues, and have no time to fix them.
Third-party dependencies are not vetted. Modern applications rely on numerous third-party components—open source libraries, commercial platforms, and cloud services. Each dependency is a potential security risk. Auditors ask: how do you manage third-party risk? How do you track vulnerabilities in dependencies? How do you ensure third-party vendors meet your security standards? Many enterprises have no good answers.
Change management is informal. Auditors want to see that changes to production systems follow controlled processes. Who approved the change? Was it tested? Was a rollback plan in place? In many enterprises, especially during development phases, change management is informal or bypassed entirely for “urgent” fixes. This shows up clearly in audits.
Compliance requirements were not mapped to technical controls. Enterprises operate under various regulatory frameworks, banking regulations, data protection laws, and industry standards. Auditors assess whether technical controls satisfy regulatory requirements. If your application must meet PCI DSS standards for payment card data, auditors will verify specific controls. If those controls were not explicitly designed in, you fail.
The cost of failing an audit extends beyond the immediate remediation work.
Launch delays have a business impact. Applications that fail security audits cannot go live until issues are resolved. Every week of delay means deferred benefits, missed revenue targets, and a competitive disadvantage. Business units that were promised new capabilities must wait. Strategic initiatives stall.
Remediation is expensive. Fixing security issues post-audit is far more costly than building correctly from the start. It requires pulling developers from other work, conducting additional testing, coordinating changes across teams, and often involves architectural rework that cascades through the system.
Stakeholder confidence erodes. When audits reveal significant security gaps, executive sponsors question the program’s management. Governance forums shift from strategic discussions to risk mitigation. Trust between business and IT deteriorates. Future programs face increased scrutiny and reduced autonomy.
Repeat audits compound costs. Failed audits lead to follow-up audits to verify remediation. Each audit consumes time, resources, and budget. Multiple audit cycles can double the effective cost of achieving compliance.
Regulatory risk increases. In regulated industries, failed audits can trigger regulatory action. Supervisory letters. Consent orders. Fines. Restrictions on business activities. The regulatory burden grows significantly when audits reveal systemic security weaknesses.
What Audit-Ready Applications Look Like
Applications that pass security audits consistently share certain characteristics. They are not necessarily the most technically sophisticated. They are the best executed.
Security controls are designed alongside functional requirements. From the earliest design phases, security requirements are as detailed as functional requirements. Authentication mechanisms are chosen. Encryption standards are specified. Access control models are defined. Logging requirements are documented. These are not afterthoughts they shape the architecture.
Documentation is created continuously, not retroactively. Every design decision is documented when made. Security assessments happen at each major milestone. Test results are recorded as tests are conducted. Change logs are maintained in real time. When the audit happens, evidence exists naturally because it was created as part of normal delivery practice.
Testing is comprehensive and ongoing. Security testing is not a pre-audit event. It is continuous. Static code analysis runs with every build. Vulnerability scans happen regularly. Penetration testing occurs at multiple stages after design, during development, and before deployment. Issues are found early when they are cheap to fix.
Third-party risks are managed proactively. Before any third-party component is used, it is vetted. Open source libraries are scanned for known vulnerabilities. Vendor security certifications are reviewed. Contractual obligations for security are established. A registry of all third-party dependencies is maintained and monitored.
Change management is formal and enforced. Even during development, changes follow a process. Pull requests require approvals. Deployments are logged. Rollback procedures are tested. Production changes require formal change tickets. This discipline creates the audit trail auditors need.
Compliance is mapped explicitly. For each regulatory requirement, there is a corresponding technical control and documentation that proves the control exists and works. If GDPR requires data subject rights, the application has mechanisms to search, export, and delete user data, plus test evidence that these mechanisms work.
Governance is clear and enforced. Someone owns security outcomes. Not just security architecture, but security delivery. This person has the authority to stop deployments if security requirements are not met. They ensure standards are followed and evidence is collected. Clear ownership prevents gaps.
The Role of Leadership in Audit Readiness
Building audit-ready applications requires more than good technical practices. It requires executive commitment and governance support.
When a CIO or CTO signals that audit readiness is a priority through how programs are structured, how performance is measured, and how accountability is enforced, the organisation responds.
This means asking the right questions in program reviews.
Not just “are we on schedule?” but “are we collecting the evidence we will need for the audit?”
Not just “is the feature complete?” but “has this feature been security tested and does it meet our standards?”
Not just “did we pass the audit?” but “what did we learn from the audit that improves our delivery process for future programs?”
Leadership also means making trade-offs. Audit readiness requires investment. Time for security testing. Budget for third-party assessments. Resources for documentation. Leaders who understand that audit failures cost far more than audit preparation make these investments without hesitation.
It also means rejecting shortcuts. When timelines are tight, there is always pressure to skip security reviews, defer testing, or push incomplete applications to production with promises to fix issues later. Leaders who hold the line on security requirements protect the enterprise from far greater costs down the road.
Building Security In From Day One
For enterprises embarking on new application development or modernisation programs, how do you build applications that are audit-ready from the start?
Begin with a security baseline assessment. Before design begins, establish what security posture you need to achieve. Which regulations apply? Which industry standards must you meet? What are the specific security controls required? This baseline becomes the foundation for all design decisions.
Define security requirements with the same rigour as functional requirements. Security requirements should be specific, measurable, and testable. Not “the application must be secure” but “the application must authenticate users using multi-factor authentication, encrypt all data in transit using TLS 1.2 or higher, and log all access to sensitive data for 90 days.”
Incorporate security reviews at each design stage. Do not wait until the design is complete to validate security. Review the conceptual architecture for security. Review the detailed design for security. Review the implementation plan for security. Early reviews catch issues when they are cheap to fix.
Use secure development frameworks and patterns. Do not build security controls from scratch. Use proven frameworks and patterns. OAuth for authentication. Established encryption libraries. Well-tested authorisation models. Building on proven foundations reduces risk and accelerates delivery.
Automate security testing in your delivery pipeline. Security testing should not be manual and periodic. Automate static code analysis to run with every build. Automate dependency scanning to detect vulnerable libraries. Automate configuration checks to ensure systems meet standards. Automation makes security testing continuous and catches issues early.
Conduct penetration testing at multiple stages. Do not wait until just before go-live to penetration test. Test early after the architecture is implemented, but before all features are built. Test again when the application is feature complete. Early testing finds design flaws. Later testing finds implementation bugs. Both are necessary.
Document as you build. Maintain architecture diagrams that reflect the current state. Document security decisions when they are made. Record test results when tests are conducted. Create runbooks for operational procedures. This documentation serves delivery teams and becomes audit evidence naturally.
Implement formal change management from the start. Even in development environments, changes should follow a process. Use pull requests with approvals. Log deployments. Test changes in non-production environments before production. Building these habits early makes them natural by the time production launches.
Track third-party components rigorously. Maintain a software bill of materials, a complete inventory of every third-party library, framework, and service the application uses. Monitor these components for security updates. Have a process to apply patches and updates promptly. This prevents vulnerable dependencies from becoming audit findings.
Plan for evidence collection. Identify early what evidence the audit will require. Architecture diagrams. Security test results. Access control matrices. Data flow diagrams. Assign responsibility for creating and maintaining this evidence. Review periodically to ensure it remains current.
Managing Third-Party and Vendor Risk
Most large enterprise applications involve external parties, development vendors, platform providers, infrastructure services, and integration partners. Each relationship is a potential audit risk.
Conduct security due diligence before engagement. Before engaging a vendor or partner, assess their security practices. What certifications do they hold ISO 27001, SOC 2, and PCI DSS? What is their incident history? How do they manage vulnerabilities? Due diligence before a contract prevents audit surprises later.
Write security requirements into contracts. Vendor contracts should specify security obligations explicitly. Which security standards must they meet? What testing must they conduct? How quickly must they patch vulnerabilities? What access will you have to audit their work? Clear contractual terms create accountability.
Require evidence of security practices. Do not just take vendors at their word. Require evidence. Ask for recent penetration test results. Request vulnerability scan reports. Review their secure development lifecycle documentation. Verify that their practices align with what they claim.
Monitor vendor security performance. Security obligations do not end when the contract is signed. Monitor vendor compliance through regular reviews. Are they applying security patches promptly? Are they reporting security incidents transparently? Are they maintaining required certifications? Poor vendor security performance should trigger escalation.
Maintain control over critical evidence. If a vendor builds parts of your application, ensure you have the evidence needed for your audit. Do not let vendors control the documentation, test results, or architecture diagrams you need. Specify in contracts that audit evidence is deliverable, and you retain copies.
Have exit strategies. If a vendor relationship ends or a vendor fails to meet security obligations, you need a plan. How will you retrieve code and documentation? How will you maintain the application without vendor support? Exit strategies prevent vendor dependencies from becoming audit blockers.
Preparing for Common Audit Scenarios
Different types of audits focus on different aspects of security. Understanding common audit scenarios helps you prepare effectively.
Regulatory compliance audits. These verify that applications meet specific legal or regulatory requirements. Banking applications may face RBI audits. Healthcare applications face audits for health data protection. Data-heavy applications face privacy regulation audits. Prepare by mapping every regulatory requirement to a specific technical control and maintaining evidence that the control exists and works.
Third-party security assessments. Large customers or partners often require security assessments before they integrate with your applications. These assess authentication mechanisms, data protection, and operational security. Prepare by documenting your security architecture clearly, conducting regular penetration tests, and maintaining current security certifications.
Internal security audits. Many enterprises conduct internal audits before external ones to identify gaps. These can be valuable preparation but only if findings are taken seriously. Treat internal audits with the same rigour as external audits. Do not dismiss findings as “just internal.”
Continuous compliance monitoring. Some regulatory frameworks require ongoing compliance demonstration, not just point-in-time audits. This means continuous security monitoring, regular control testing, and periodic reporting. Prepare by building monitoring and reporting into operational processes from day one.
Post-incident audits. After a security incident, regulators or internal audit teams may conduct focused reviews. These assess what went wrong, whether controls failed, and what remediation is needed. Prepare by maintaining comprehensive incident logs and having a well-documented incident response process.
Choosing Partners Who Understand Audit Requirements
For most large enterprises, delivering complex applications means working with external partners. The partner you choose significantly influences your audit readiness.
When evaluating potential partners for enterprise program management or IT transformation strategy, audit readiness should be a key selection criterion.
What is their track record in regulated industries? Partners who have delivered applications for banking, healthcare, insurance, or government sectors understand audit requirements deeply. They have built audit-ready applications before. They know what evidence auditors need and how to collect it.
How do they embed security in their delivery process? Look for evidence of security-first delivery. Do they conduct threat modelling during design? Do they automate security testing in their pipelines? Do they maintain security test environments? Partners with mature security practices produce audit-ready applications naturally.
What documentation do they provide? Ask what documentation comes as a standard deliverable. Architecture diagrams? Security assessment reports? Test results? Configuration documentation? Partners who understand audit requirements provide comprehensive documentation without being asked.
How do they handle findings during delivery? Security issues will be discovered during development. What matters is how partners respond. Do they triage findings appropriately? Do they track remediation? Do they retest after fixes? A partner’s finding management process predicts audit readiness.
Can they support audit preparation and response? The best partners do not disappear when the audit begins. They participate in audit preparation, provide evidence, answer auditor questions, and support remediation if findings occur. Firms like Ozrit, which partner with enterprises on large-scale digital transformation, understand that delivery includes audit readiness and remain engaged through compliance validation.
Creating Audit Evidence That Actually Helps
Not all audit evidence is equally useful. Effective evidence is clear, current, and demonstrates actual practice, not just policy.
Architecture diagrams should reflect reality. Many enterprises have beautiful architecture diagrams created at project start. But if the implementation diverged from the design, the diagrams would mislead auditors. Keep architecture documentation current. Update it when changes occur. Use tools that generate diagrams from actual infrastructure where possible.
Security policies need implementation evidence. Having a policy that says “all data in transit must be encrypted” is not enough. Auditors want evidence that encryption is actually implemented. Provide configuration files, network diagrams, and test results that prove the policy is followed in practice.
Test results should be specific and complete. Generic test reports that say “security testing was conducted” do not satisfy auditors. Provide detailed results of what was tested, what methodology was used, what was found, what was fixed, and what remains. Complete test evidence demonstrates thoroughness.
Access control matrices should match the implementation. An access control matrix documents who can access what. But if the matrix does not match actual system permissions, it reveals a control gap. Regularly audit actual access against documented permissions and correct discrepancies.
Change logs should explain the what and why. Change logs that list what changed are basic evidence. Better evidence explains why the change was made, who approved it, what testing was done, and what the rollback plan was. This demonstrates controlled change management.
Incident logs should be comprehensive. Document all security incidents, even minor ones. What happened? How was it detected? How was it contained? What was the root cause? What remediation was implemented? Comprehensive incident logs show mature security operations.
Learning from Audit Findings
Even well-prepared applications may receive audit findings. What separates mature enterprises is how they respond.
Triage findings appropriately. Not all findings are equal. Some are critical vulnerabilities requiring immediate remediation. Some are control weaknesses that need fixing before production. Some are documentation gaps that can be addressed more gradually. Triage based on risk and impact, not just auditor severity ratings.
Understand root causes, not just symptoms. If auditors find that access controls are insufficient, the root cause may not be technical it may be that requirements were unclear, that testing was inadequate, or that change management was bypassed. Fixing the symptom without addressing the root cause ensures the problem recurs.
Remediate systematically. Create a remediation plan with owners, timelines, and validation steps. Track progress rigorously. Do not let remediation drift. Communicate progress to stakeholders and auditors. Systematic remediation demonstrates commitment and competence.
Validate that fixes work. After remediating findings, test that the fixes are effective. Conduct follow-up scans. Retest controls. Have a different team validate. Self-assessed remediation often misses issues. Independent validation ensures fixes are complete.
Update processes to prevent recurrence. If audit findings reveal process gaps, inadequate security reviews, missing documentation, or insufficient testing, update your delivery processes. Add checkpoints. Improve templates. Enhance training. Process improvements prevent the same findings in future audits.
Share learnings across the organisation. Audit findings from one program are often relevant to others. Share learnings. Update enterprise standards. Brief other teams. Institutional learning turns individual audit findings into organisation-wide improvement.
Building Long-Term Audit Readiness
Applications are not static. They evolve through enhancements, integrations, and operational changes. Audit readiness is not a one-time achievement it is an ongoing practice.
Maintain security hygiene continuously. Apply security patches promptly. Update vulnerable dependencies. Review access permissions regularly. Security hygiene that lapses between audits creates avoidable findings.
Keep documentation current. As the application changes, update documentation. New features change the architecture. New integrations change data flows. New configurations change security posture. Documentation that falls out of date becomes a liability in audits.
Conduct periodic self-assessments. Do not wait for external audits to assess security. Conduct internal security reviews regularly. Treat them seriously. Remediate findings before external audits. Self-assessment makes external audits validation exercises, not discovery exercises.
Monitor regulatory changes. Regulations evolve. New requirements emerge. Existing requirements are reinterpreted. Monitor the regulatory landscape relevant to your industry and geography. Assess the impact on your applications. Update controls proactively.
Invest in tooling that supports audit readiness. Security information and event management systems, configuration management databases, and automated testing platforms. These tools make audit readiness more efficient. They provide visibility, automate evidence collection, and reduce manual effort.
Treat audit readiness as a competency. Enterprises that repeatedly build audit-ready applications develop institutional competency. They have documented processes, trained people, reusable templates, and lessons learned. This competency becomes a competitive advantage—they deliver faster because they do not struggle with audit remediation.
The Hidden Value of Audit-Ready Applications
Most enterprises view audit readiness as compliance overhead. Something required but not valuable. This misses the larger point.
Applications built to pass audits are better applications.
They have clearer architecture because security considerations force design discipline. They have better documentation because audit requirements demand it. They have more robust testing because security validation is comprehensive. They have stronger governance because accountability is explicit.
These qualities benefit the business beyond compliance.
Better architecture means easier maintenance and evolution. Better documentation means smoother operational handoffs. Better testing means fewer production issues. Stronger governance means more predictable delivery.
Audit-ready applications are also more trusted by customers, partners, and regulators. Trust enables business relationships. It accelerates partnerships. It reduces regulatory friction. In markets like India, where regulatory scrutiny is increasing and customer awareness of security is growing, audit readiness differentiates market leaders from the rest.
Final Thoughts
Building enterprise applications that pass security audits is not about satisfying auditors. It is about building applications properly.
The same practices that create audit readiness create better applications, disciplined design, comprehensive testing, clear documentation, and strong governance.
Enterprises that treat audits as crises will continue to experience them as stressful, expensive, and disruptive events that delay launches and erode confidence.
Enterprises that treat audit readiness as a delivery standard will experience audits as validation expected checkpoints that confirm what the team already knows: the application is secure, well-documented, and ready for production.
For C-level executives overseeing enterprise software delivery or managing complex IT programs, the choice is clear.
You can build applications and hope they pass audits. Or you can build applications designed to pass audits.
The first approach leads to remediation cycles, delayed launches, and stakeholder frustration.
The second approach leads to smooth audits, confident launches, and organisational trust.
Because in enterprise execution, audit readiness is not overhead. It is discipline. And that discipline, practised consistently, is what separates successful programs from struggling ones.